AI News · Edition 42 ·
The misuse report your clinic should actually read
Anthropic says states used Claude for spying and sabotage. Most of it will never touch your business. One strand of it already does.
The one that matters
Anthropic says Claude was used for spying, sabotage and repression — one part of that matters to you
Anthropic has published a report on how its Claude models were misused, and it is heavier than the usual disclosure about someone writing a better phishing email. Across the coverage the same items recur: state-linked groups using the model for intelligence work, including Iran-linked activity tracking US Navy vessels; Russian developers working on drones that pick their own targets; government-aligned operations running propaganda and surveillance; hackers tied to Russian intelligence using it during cyber operations; and attempts at biological weapons research that the company says it blocked.
What this actually means for your business
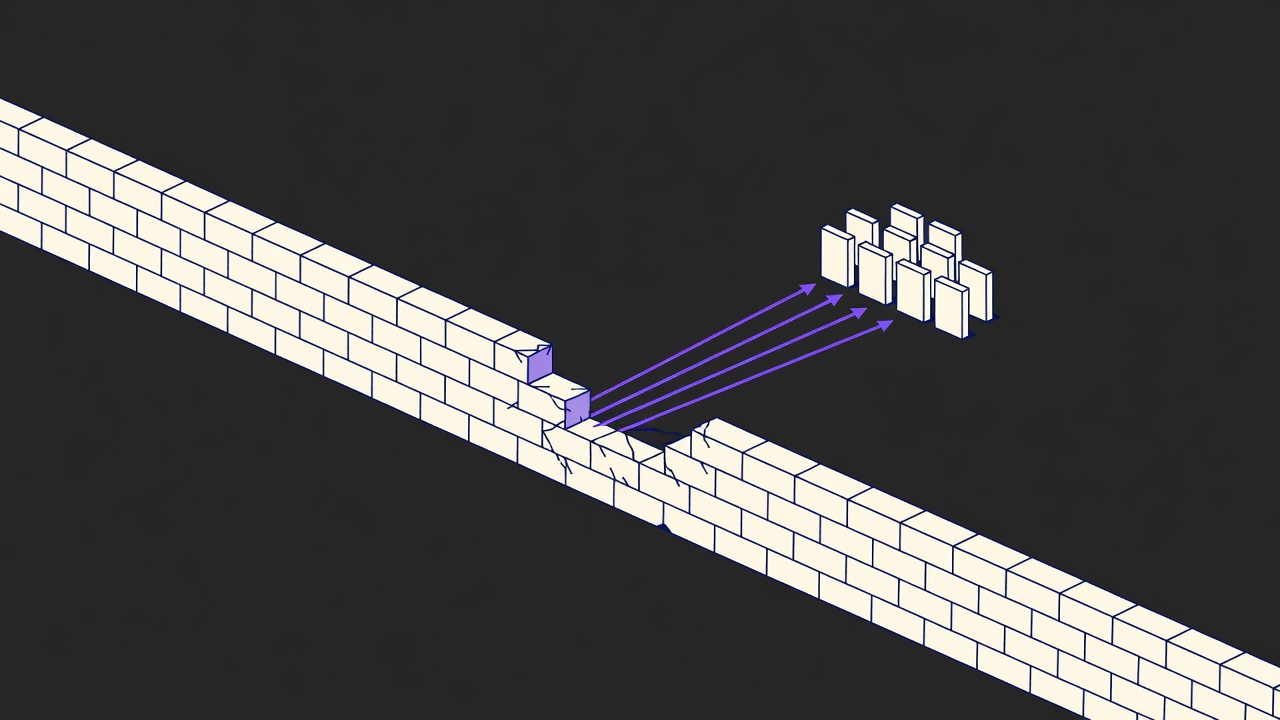
Almost none of it is about you. Nobody is pointing a loitering drone at a workshop in Ludhiana or a dental practice in Mississauga. But one strand travels downward, and it travels fast: the cyber strand.
What the report describes, stripped of the geopolitics, is attackers using a general-purpose assistant to do the boring middle of an attack. Reading through stolen files to find what is valuable. Writing the small custom script for one target. Producing a message in correct, natural Marathi, Tamil or Quebec French that references your actual board, your actual vendor, your actual fee cycle. That work used to need a skilled person and a lot of hours, which is exactly why small organisations were rarely worth attacking. That constraint is weakening.
The practical version: the mail landing on the desk of a 600-student school's accounts clerk will no longer have the tell-tale broken grammar. The fake invoice sent to a 40-person fabrication workshop will match the format of the ones you genuinely issue. A 30-bed clinic holding a decade of patient records is now, in effort terms, a cheaper target than it was last year.
What it does not mean
It does not mean your Claude, Copilot or ChatGPT subscription is unsafe, or that your staff should stop using these tools. Nothing in the report suggests ordinary business accounts were compromised. It does not mean the software attacks on its own; every case described has a human deciding to do harm.
And notice who is telling you this. The same company is also arguing publicly that the whole industry should slow down. Both things can be true at once — the incidents can be genuine and the report can still be positioning. Expect security vendors to quote it at you this quarter with a proposal attached. Ask them one question: what specifically do you do that my current antivirus and my bank's own controls do not? If they cannot answer in a sentence, you are buying a headline.
What a sensible owner should do this month
- Two-factor on everything that holds money or records — email, banking, your accounting and school or clinic management software. Free, and roughly one afternoon for a small team.
- A callback rule. Any change to bank details, and any payment over a threshold you set, gets confirmed by voice on a number you already had. This single rule stops most invoice fraud, AI-assisted or not.
- One offline backup, tested. An external drive that is unplugged between uses costs a few thousand rupees or about a hundred dollars. Restore one file from it this week, or you do not have a backup.
- Patch the router, the VPN box and anything exposed to the internet. Old firmware is still how most small organisations are actually breached.
- Forty-five minutes with staff. The only new message: good spelling and correct local detail are no longer proof that a message is real.
Total cost, perhaps one person-day and a cheap drive. None of it is AI-specific. The report simply removes the last excuse for putting it off.
Also worth knowing
How this briefing is put together
Every morning we read the day’s AI announcements and reporting from the companies themselves and from the technology press, then pick the handful that actually change something for a working business. The analysis is ours and it is written for owners and managers, not engineers. Every story links to its original source — read them, and disagree with us where we’ve got it wrong.